HunterX
Not just another scanner. HunterX combines reconnaissance, security tooling, AI-assisted reasoning, vulnerability validation, PoC generation and validation, evidence collection, correlation, and report generation into one workflow.





HunterX v7 Overview
From AI-assisted reasoning and hypothesis generation to validated findings, minimal safe PoCs, reproducible proof and report-ready output.
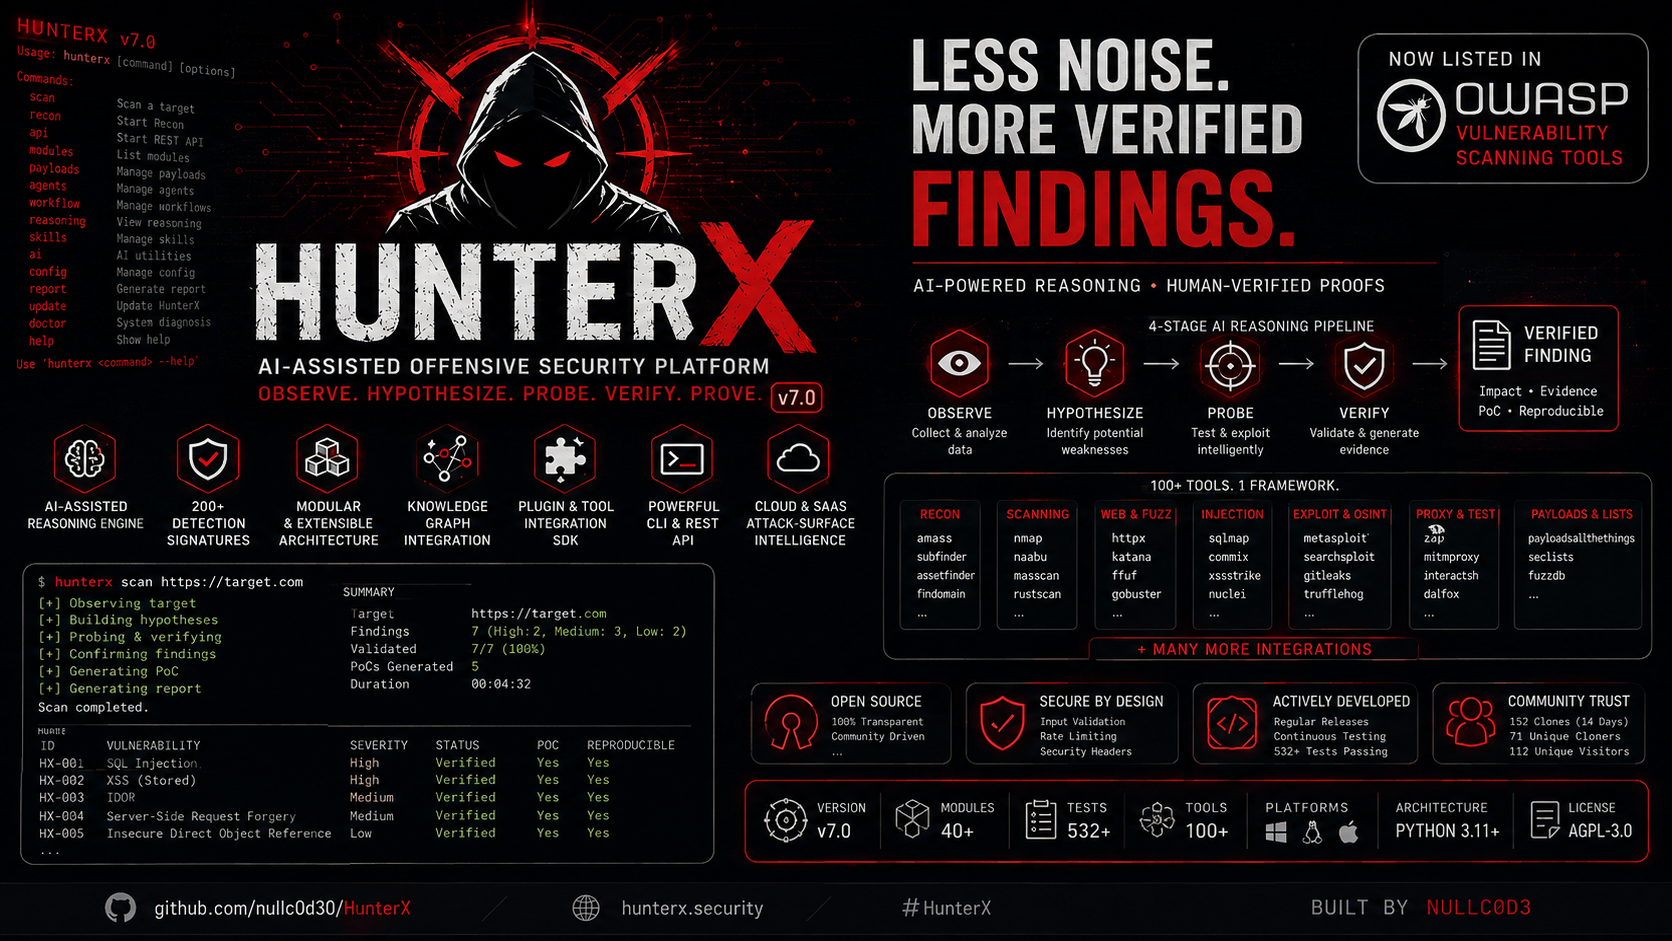
Why HunterX?
HunterX is not designed merely to tell you that a vulnerability might exist. It takes the investigation further — DISCOVER → REASON → TEST → VERIFY → PROVE → GENERATE PoC → VALIDATE → REPORT.
| Capability | Traditional Scanner | HunterX v7 |
|---|---|---|
| Output | Candidate / “Possible” finding + confidence | Validated finding + evidence + reproducibility + impact + PoC |
| Validation | Signature match | Evidence-driven hypothesis testing & proof contracts |
| PoC | — | Minimal safe PoC generation, replay & validation |
| Reporting | Raw JSON | Report-ready: Markdown, HTML, JSON, SARIF, PDF, package |
| Tooling | Single engine | Orchestrates 92 open-source security tools |
| Intelligence | — | Target intelligence, cloud/SaaS intelligence, knowledge graph |
Less noise. More verified findings.
From Detection to Proof
A vulnerability detection is not a validated finding. HunterX carries every candidate through the full investigation.
  SQL Injection
     ↓
  Affected asset
     ↓
  Endpoint
     ↓
  Parameter
     ↓
  Observed behavior
     ↓
  Verification
     ↓
  Evidence
     ↓
  Minimal reproducible PoC
     ↓
  PoC validation
     ↓
  Impact assessment
     ↓
  Report-ready finding
Vulnerability + Evidence + Reproducibility + Impact + PoC = Validated Finding
How HunterX Works
HunterX orchestrates the security-tool ecosystem — it reasons, correlates, verifies, proves and reports, rather than replacing the tools you already use.
  DISCOVER
     ↓
  FINGERPRINT
     ↓
  REASON
     ↓
  HYPOTHESIZE
     ↓
  PROBE
     ↓
  VERIFY
     ↓
  PROVE
     ↓
  POC
     ↓
  REPLAY
     ↓
  CORRELATE
     ↓
  REPORT
Security Coverage
Discovery, validation and proof across the vulnerability classes HunterX is designed for.
Web Application Security
SQL/NoSQL injection, XSS, SSTI, XXE, path traversal/LFI, command-injection indicators, open redirect, CORS and security misconfiguration.
API & GraphQL Security
API discovery, OpenAPI/Postman parsing, GraphQL introspection, broken access control (IDOR/BOLA), authentication and authorization.
Cloud & SaaS Attack Surface
Provider detection, cloud resource intelligence, exposure/environment classification and topology for AWS, Azure, GCP, OCI, Cloudflare and more.
Network & Infrastructure
Port/service/version discovery, OSINT, DNS intelligence and live-host service discovery orchestrated through the toolchain.
Secrets & Code Analysis
Secret scanning (Gitleaks, TruffleHog, detect-secrets), SAST (Semgrep) and dependency scanning for source/code assessments.
Novel / Unknown Behavior
Hypothesis-driven discovery and investigation of unknown or application-specific behaviors — without claiming guaranteed zero-day discovery.
Built to Work With the Security Tooling Ecosystem
HunterX orchestrates the ecosystem rather than owning every security capability itself.
Recon / Asset Discovery
Amass, Subfinder, Assetfinder, Findomain, DNSx, MassDNS, Shuffledns, theHarvester, BBOT and more.
Network / Port Scanning
Naabu, Nmap, Masscan and RustScan.
HTTP / Crawling / Discovery
HTTPx, WhatWeb, Katana, Gospider, Hakrawler, GAU, Waybackurls and URLFinder.
Fuzzing / Content Discovery
FFUF, Feroxbuster, Gobuster and Dirsearch.
Parameter / Endpoint Discovery
Arjun, ParamSpider, Kiterunner, LinkFinder, SecretFinder and xnLinkFinder.
Vulnerability Detection / Validation
Nuclei, Dalfox, XSStrike, SQLmap, Ghauri, Commix, Interactsh, Tplmap, SSTImap, XXEinjector, GraphQLmap and InQL.
Source / Code / Secret Analysis
Gitleaks, TruffleHog and Semgrep.
Proxy / Web Security
OWASP ZAP and mitmproxy.
Exploitation / Security Research
Metasploit, SearchSploit and ExploitDB.
Knowledge / Payload Resources
PayloadsAllTheThings, SecLists and FuzzDB.
PoC & Validation
Proof is part of vulnerability validation — not an afterthought.
  HYPOTHESIS → PROOF CONTRACT → REQUIRED EVIDENCE → MINIMAL PROOF
  STRATEGY → PROOF CONSTRUCTION → SAFETY VALIDATION → SCOPE
  VALIDATION → EXECUTION → REPLAY → EVIDENCE EVALUATION →
  IMPACT → CONFIDENCE → VALIDATED FINDING → REPRODUCTION PACKAGE
  → REPORT
Proof Contracts
Per-class contracts define preconditions, allowed/forbidden actions, required evidence and expected behavior for SQLi, XSS, SSRF, LFI, IDOR, SSTI, XXE and more.
Replay & Reproducibility
PoCs are replayed deterministically; reproducibility requires repeated successful replays — never a single run.
Evidence-Driven Impact
Impact is classified strictly from captured evidence; confidence is a versioned, weighted policy over named factors — never a universal percentage.
Safety-by-Design
Minimal safe proofs. No data destruction, persistence, reverse shells, DoS or mass data extraction is ever scheduled.
Target Intelligence
HunterX maintains structured target intelligence instead of treating every scan as an isolated command.
Assets & Targets
A persistent view of the surface under assessment.
Observations & Findings
Canonical, normalized results from every tool run, correlated into findings.
Evidence & History
Provenance-backed evidence and target snapshots, diffs and change detection.
Relationships & Topology
How assets, services and cloud resources relate — feeding correlation.
Mission State
Checkpoint/resume, campaign state and tool-result records.
Cloud Intelligence
Cloud/SaaS attack-surface intelligence persisted alongside target data.
Cloud & SaaS Intelligence
Evidence-backed cloud and SaaS attack-surface intelligence for authorized targets.
Provider Coverage
AWS, Azure, GCP, OCI, Cloudflare, DigitalOcean, Akamai, Fastly, Vercel, Netlify, Heroku, Render, Fly.io, Supabase, Firebase, Kubernetes and Docker.
Topology
Account/region/resource relationships and cloud architecture edges.
Exposure & Environment
Exposure classification and production/staging/dev environment classification.
Passive by Design
Built from static evidence (DNS, TLS, HTTP headers, HTML/JS, OpenAPI). Never authenticates to cloud accounts, never accesses cloud resources, never retrieves secrets.
Knowledge Graph & Attack Paths
HunterX correlates results across tools and missions into a knowledge graph of entities and relationships — enabling cross-scan correlation, attack-path analysis and context-aware reasoning.
Targets ↔ Assets ↔ Observations ↔ Findings ↔ Evidence ↔ Proofs ↔ Attack Paths
Reporting
The workflow does not end at detection. HunterX turns validated findings into structured, professional reports.
Markdown & HTML
Human-readable findings and visual dashboards.
JSON & SARIF 2.1
Machine-parsable output; VS Code / GitHub CodeQL integration.
PDF & Packages
Document export and ZIP evidence bundles.
Report Contents
Finding, asset, endpoint, parameter, evidence, verification, PoC, reproduction, impact, confidence, relationships, risk/context and remediation where supported.
Who Uses HunterX
An AI-powered offensive security platform for the people doing authorized security work.
Bug Bounty Hunters
Evidence-backed findings, minimal reproducible PoCs and report-ready packages.
Penetration Testers
Structured missions, professional reports, remediation and retest planning.
Red Teams
Mission orchestration, attack-path planning, cloud/SaaS intelligence and correlation.
Security Researchers
Hypothesis-driven investigation of unknown and application-specific behaviors.
Application Security Engineers
Validated findings with PoC, impact and confidence instead of candidate noise.
DevSecOps & Security Teams
CI/CD integration, SARIF, REST API and reproducible results.
Architecture
A Clean Architecture Python core with clear component responsibilities and defined communication interfaces.
                +-----------------------------+
                |  CLI / API / Docker          |
                +-----------------------------+
                           |
                +-----------------------------+
                |  Mission & Workflow Engines  |
                |  Orchestrate → Reason →      |
                |  Validate → Prove → Report   |
                +-------------+---------------+
                           |
                +-----------------------------+
                |  Toolchain Intelligence      |
                |  92 tools · SDK · Parser/  |
                |  Normalizer · Chaining      |
                +-------------+---------------+
                           |
                +-----------------------------+
                |  Proof / PoC Engine          |
                |  Contracts · Replay ·      |
                |  Reproducibility · Impact   |
                +-------------+---------------+
                           |
                +-----------------------------+
                |  Target Intelligence & TIDB  |
                |  Assets · Findings ·         |
                |  Evidence · Cloud · Topology |
                +-------------+---------------+
                           |
                +-----------------------------+
                |  Knowledge Graph & Events    |
                |  Correlation · Attack Paths |
                +-------------+---------------+
                           |
                +-----------------------------+
                |  Reporter                   |
                |  MD / HTML / JSON / SARIF / |
                |  PDF / package              |
                +-----------------------------+
Integrations
HunterX integrates with the open-source security ecosystem and your pipeline.
Security Tools
92 registered tools across recon, scanning, crawling, fuzzing, parameters, validation, secrets, SAST, proxies, exploitation and knowledge resources.
AI Providers
OpenAI, Anthropic/Claude, DeepSeek, OpenRouter, Google Gemini and xAI/Grok — provider and model selected independently, each with its own API key and endpoint.
CI/CD
Docker images, SARIF export for GitHub CodeQL, and a REST API for pipeline integration.
Persistence
SQL (SQLite default, PostgreSQL supported) via TIDB with Alembic migrations.
Enable AI in HunterX
AI is optional. Configure HunterX AI providers, API keys, models, environment variables, and Docker usage in minutes.
Optional by Design
HunterX runs without an API key using a safe fallback. Add AI only when you want AI-assisted reasoning.
Private .env
Copy .env.example to .env, add your provider, model and key. The file is gitignored and never committed.
Docker Ready
Supply keys at runtime with docker run --env-file .env — never bake secrets into an image.
Community
HunterX is open-source and community-driven. Apache 2.0 licensed.
Installation
Requirements: Python 3.11+ on Linux, macOS or Windows.
pip install hunterxsec
Responsible Use
HunterX is an authorized cybersecurity testing and research platform. It is designed to be used only against systems you own or are explicitly authorized to test. You are responsible for obtaining appropriate authorization before testing any system and for complying with all applicable laws and terms of service.
About HunterX
HunterX is created and maintained by Ahmed Awad (AKA NullC0d3). The canonical project is the GitHub repository nullc0d30/HunterX.
👤 Author
Ahmed Awad (NullC0d3) — Cybersecurity Threat Intelligence Analyst and open-source developer. Creator and maintainer of HunterX.
🎯 Mission
Democratize intelligent vulnerability assessment by combining AI-assisted reasoning with evidence-driven validation, proof and reporting in a single, extensible open-source platform.
🛰 Responsible Use
HunterX is provided exclusively for authorized security testing. Users are solely responsible for obtaining authorization before scanning any target.
📖 License
Released under the Apache License, Version 2.0. Free to use, modify, and distribute for any purpose.